Chainflip loses $12 million to apparent key compromise

An attacker drained $12 million from the Chainflip cross-chain swap protocol. They then immediately swapped the tokens to ETH and then laundered the assets through Tornado Cash to make them impossible for stablecoin issuers to freeze and more challenging for investigators to trace.

The transaction was signed with the protocol's signing key, suggesting that the key may have been compromised. It's not clear how that would have happened, given that the key is rotated every three days, and each of the protocol's 150 validators is only supposed to have access to a portion of the key. 100 out of the 150 are needed to sign transactions.

In a message to the attacker, Chainflip revealed that the total theft was around $12 million — considerably higher than early estimates by blockchain researchers of around $4.9 million. Chainflip also said they had "identified the mechanism of key exposure and have prevented such future attacks", though they have not published their findings.

Chainflip offered a 10% "bounty" for the return of the funds, and threatened the thief with law enforcement action.
K3 Capital's yield-bearing sBOLD vault drained in flash loan attack

Attackers using flash loans drained nearly the entire $3.43 million from a yield-bearing Ethereum vault run by K3 Capital. They exploited a bug in the vault's pricing logic that ignored collateral it held below a set amount, allowing an attacker to deposit small amounts of wETH that weren't counted toward the pricing calculations. They then were able to swap those deposits into BOLD, a dollar-pegged stablecoin, causing prices to increase and allowing them to cash out larger and larger amounts.

After the original theft transaction, a series of copycats joined in, and the vault was drained within minutes. K3 Capital paused the vault 40 minutes after the first transactions, well after the money was gone.

K3 Capital has published a "recovery plan" that largely consists of "ask the attackers nicely to return the funds". After that, it plans to divvy up whatever assets it gets back among investors in the vault — likely far below what they put in.

K3 Capital describes itself as "one of the largest crypto-native asset managers". It was co-founded by Kiril Nikolov, formerly of Nexo, in 2021.

Lighter user(s) exploited for $15 million

An attacker drained at least one market maker account on the perpetual futures exchange Lighter. One account was emptied of around $10.4 million, and another may have lost about $5.1 million, according to blockchain researchers. Lighter has attributed the theft to a "leaked API key for a specific trader's account", though they did not confirm the amounts stolen or address researchers' identification of a second affected account.

Lighter's security council activated "Guardian mode", pausing withdrawals, which they say prevented the attacker from cashing out about $5 million of the assets. However, the attacker was still able to swap $10.4 million of the stolen assets to ETH.

Kava Lend exploited for $3.8 million

An attacker drained around 55.2 million KAVA (about $3.8 million) from Kava Lend, the Kava blockchain's native lending protocol. Kava Lend had continue to offer a BUSD-based lending market years after Paxos stopped minting the Binance-branded stablecoin, and most activity had dried up.

The attacker was able to take advantage of this by first pushing the market's net supply down to a tiny fraction of a cent, where a rounding error then caused the protocol to count each BUSD deposit as worth roughly 243,000 times its real value. The attacker then took out 127 loans against the erroneous value. The attacker quickly bridged most of the tokens to BNB Chain dumped them for about $2.1 million.

DataVault AI's stock crashes after it says it can't access its own bitcoin

Datavault AI markets itself as a "data sciences" and "Web 3.0" company that is "harnessing the power of supercomputing to subordinate AI" but also apparently working on real-world-asset tokenization (including an attempt to tokenize a fleet of AI data centers) but also I guess developing audio technology for live events and data-over-sound applications. Outside of their own press releases, it looks like their business plan is mostly to just hold bitcoin, use a lot of fancy buzzwords, and hope their stock price goes up.

Or at least that was the plan, until they disclosed in an SEC filing that that bitcoin may never have been theirs. It came from a September 2025 deal in which pain medication and, apparently, crypto treasury company Scilex Holding bought around 279 million Datavault shares for $150 million in BTC. Rather than sending any coins on-chain, Scilex just credited around 1,309 BTC to Datavault's account at the little-known Biconomy exchange. Biconomy had itself paid Scilex in bitcoin for $200 million of stock in a Scilex subsidiary just days earlier. On October 26, Datavault disclosed that it hasn't been able to withdraw the bitcoin since June. Neither Datavault nor Biconomy has explained why Datavault was unable to complete the withdrawal. Datavault has told the SEC it intends to restate its financial statements for every period since the transaction, and warned that without the bitcoin on its books, it may not be able to stay in business.

The stock halved the next day, to around 7¢, down from more than $2 a year earlier. Since then, the board has ousted founder and CEO Nathaniel Bradley, who is now suing the company, and Nasdaq has suspended trading in the stock for failing to meet its minimum share price.

Initia suffers second exploit less than a month after the last

On November 2, as the project came back online from a $2.7 million exploit, Initia tweeted "We are so back." On November 10, the Initia networks were once again halted after another hack, this time in which an exploiter stole $3.27 million. According to Initia, the attacker exploited a command-injection vulnerability using a compromised Google Cloud key, which exposed environment variables and granted them access to Initia's GitHub and other cloud accounts. From there the attacker got into Anvil, the platform that hosts Initia's rollups, and approved fake withdrawals that released escrowed assets.

Initia said about $2.16 million of what was taken was frozen when the project again halted its layer-1 chain. At least $615,000 of the remaining amount was sold on Initia's DEX and withdrawn. As with the first hack, Initia kept its blockchains offline for an entire ten days. Although they posted that they had spent the time "harden[ing] security at every layer of the stack while auditing and rebuilding our infrastructure alongside security professionals", the response was less than enthusiastic: "No body cares its finished" and "scam".

Initia is backed by Binance Labs, Delphi Ventures, and at least six others. The company, started by ex-Terraform Labs developers raised an undisclosed amount of pre-seed funding from Binance Labs in October 2023. In February 2024 they raised a $7.5 million seed round, and they raised another $14 million in a Series A round in September of that year. However, the project's TVL has plummeted from its $40 million peak in May 2025 to below $3 million for most of 2026.

Mercado Bitcoin halts withdrawals after $40 million hack

Brazil's largest crypto exchange, Mercado Bitcoin, suspended deposits and withdrawals on November 2, citing a security incident. Researchers have estimated the loss at about $49 million, though around $10 million was frozen by centralized stablecoin issuers. The exchange has said it will cover the loss from its own funds.

The attacker emptied hot wallets across at least ten blockchains in roughly 25 minutes. A second wave of attacks drained customer deposit addresses on Ethereum, and those transfers continued for about four hours after the exchange said the incident had been contained.

French bank Crédit Mutuel Arkéa hit in $133M crypto theft

Blockchain investigator ZachXBT posted on November 2 that an EU entity had lost over $106 million from accounts at several crypto exchanges on November 1, with funds withdrawn in the USDC and USDT stablecoins. He later added a further $27 million in exchange withdrawals tied to the theft, bringing his estimate above $133 million.

According to ZachXBT, the attacker swapped USDC for ETH, moved funds through instant exchanges, converted some into the Monero privacycoin, and bridged funds across multiple chains to make them harder to trace. He accused the institution of not having made "proper incident disclosure", which he said let approximately $30 million in stolen funds go unfrozen by law enforcement when they could have been recovered.

A day later, the French bank Crédit Mutuel Arkéa confirmed it had been hit by a cyberattack that allowed "fraudulent operations", but did not mention crypto. The bank, which has been preparing to enter the crypto sector, later told Reuters that around €100 million ($112.6 million) had been stolen via "fraudulent transactions", and that the funds were not originally in the form of cryptocurrency but may have been swapped to crypto after the theft.

Polymarket users' funds stolen, again

Polymarket users have lost a combined, estimated $2.65 million after a Polymarket exploit. The company acknowledged there had been "an incident" and put the site into "cancel-only" mode, meaning that all bets were disabled outside of cancelling them. They later, once again, claimed that the issue is due to the compromise of a "third-party provider", and re-enabled trading after about an hour.

This is the second time Polymarket users have lost funds due to exploits Polymarket has blamed on third-party vendors. In June, customers lost almost $3 million after a malicious script was injected into the frontend. They reimbursed user losses then, and have said they will do the same in this incident as well.

North Korea hacks Binance for around $6.3 billion, some frozen

Binance has confirmed that an attacker exploited the exchange, stealing around $6.3 billion from multiple hot wallets. The theft has set the new record for the largest crypto theft.

Luckily for Binance, Tether and Circle quickly began freezing some of the exploiter's wallets. Tether froze at least $1.567 billion of the roughly $1.768 billion in stolen USDT, and Circle froze around $800 million of the $823 million in USDC. Binance estimated that $3 billion in total was frozen, though some other networks that have frozen assets are preventing the attacker from cashing out, but may not be able to easily restore them to Binance.

Binance founder Changpeng Zhao, who is not legally allowed to run the exchange yet seems to remain very closely aware of its inner workings, posted early estimates of the freezes and wrote, "I don’t manage Binance (.com) anymore, but as a shareholder, I expect all user funds will be fully covered." He later added, "Loss might be a bit higher than [$1 billion], but will cover." Binance later disclosed that they believed the exploit occurred after a devops employee's laptop was compromised.

Blockchain security firm TRM Labs subsequently attributed the attack to TraderTraitor, a North Korean state-sponsored cybercrime group also known as the Lazarus Group. They have been behind many of the largest cryptocurrency thefts, including the now second-largest hack of all time: the 2025 theft of $1.5 billion from the Bybit exchange.

Initia suffers $2.7 million loss after unauthorized mint exploit

The Initia project halted its blockchain after an attacker was able to exploit a vulnerability in the project smart contract to perform an unauthorized mint of unbacked wrapped tokens. The attacker then bridged the tokens off Initia's chain to cash out. They ultimately made off with approximately $2.7 million in proceeds from minting fake versions of AUSD, ETH, and USDC on the Initia chain and then converting it to ETH.

The project subsequently announced that its associated foundation would be covering the stolen assets to ensure all assets on the chain were fully backed. The project brought its blockchains back online on November 2, after spending a massive ten days halted. "We are so back," they announced on Twitter.

CoinDCX admits $16 million theft after claiming it was a "false alarm"

Indian exchange CoinDCX confirmed a loss of 15.99 million USDT, saying an automated process had failed to move customer deposits out of wallet infrastructure it had retired following its July 2025 breach. The exchange said it absorbed the loss itself and that customer balances would be unaffected.

Before admitting the loss, co-founder Sumit Gupta refuted crypto investigators' concerns about a hack, writing on Twitter that CoinDCX's wallets were "not breached" and calling the activity a "false alarm". The exchange later blamed the incident on an internal process failure.

The loss adds to the roughly $44 million CoinDCX suffered in a July 2025 hack it initially attributed to a server breach, which was later connected to a compromised engineer laptop.

Keystone to destroy 18,835 hardware wallets after website breach

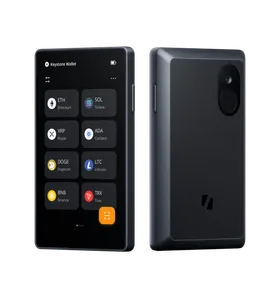
Product photo of the Keystone 3, which resembles a smartphone and displays several cryptoasset logos on the screenKeystone 3 product photo (attribution)
Hardware wallet maker Keystone said it will destroy 18,835 unsold devices and suspend shipments after a website breach on October 20 exposed customer data and an authentication key built into its devices during production.

An attacker gained access through a flaw in a third-party data monitoring tool. Keystone said the breach did not expose recovery phrases, private keys, or wallet credentials, but the stolen authentication key means counterfeit devices could pass online authenticity checks. Keystone said it would replace the key in new devices. They said that devices delivered before October 20 remained safe to use if they pass authentication, but urged caution for customers who received devices using the old key after that date.

Cysic bridge exploited

A bug with the Cysic bridge let an attacker mint 10 million Cysic (CYS) tokens on BNB Chain. Cysic suspended the bridge and blacklisted the recipient address, freezing about 2.8 million of the minted tokens. The project attempted to recoup some of the stolen assets by offering a 10% "bounty". Instead, the attacker moved sent substantiall all of the stolen funds they'd been able to cash out — about $744,000 — to Tornado Cash, making Cysic's chances of recovering the assets much slimmer.

Cysic is a blockchain-based marketplace for computing resources, and is backed by Polychain Capital, OKX Ventures, and Hashkey Capital.

AI-focused Qubic blockchain halts after weak wallet seeds enable $1.4 million in thefts

The Qubic "true decentralized intelligence" project, an artificial intelligence-focused blockchain, halted on October 17–18 after an attacker exploited weakly generated wallet seeds to drain around 2.94 trillion QU (about $1.4 million) from 1,404 wallets.

Qubic said the attack was enabled by a flaw affecting wallet seeds created in its web wallet on an iPhone or iPad in any browser, in Safari on a Mac, or in the Qubic iOS app before July 2025. A third-party analysis traced the cause to Qubic's use of JavaScript's insecure Math.random() function.

Qubic said 87% of the drained funds never left the network and were frozen. The remaining 13% was sent to the MEXC exchange; Qubic says the exchange froze the receiving account within about an hour. Qubic later performed a blockchain rollback and opened a recovery process for affected holders.

Blur NFT marketplace to shut down

Blur, the NFT marketplace that overtook OpenSea in trading volume shortly after its 2022 launch, announced it will shut down its website in a month. They also announced that Blend, Blur's NFT lending platform, will stop matching new loans on the same day. Borrowers have until then to repay their loans or let them default.

The announcement comes days after the Blur team said it would also shut down Blast, its Ethereum layer-2 blockchain, because it cost more to run than it earned.

At least $86 million stolen via tampered Ledger hardware wallets resold by CryptoBilis

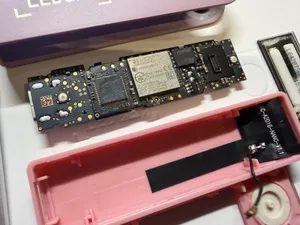
A Ledger hardware wallet that has been opened to reveal the original chip, plus an additional chip with an antenna that was added by an attackerA tampered Ledger device (attribution)
The users of more than 300 Ledger cryptocurrency wallets have suffered an estimated $86 million to $93 million in losses after thieves drained assets across blockchains including bitcoin, Ethereum, and Tron. Ledger is a popular manufacturer of hardware wallets — a type of physical, offline device used to store cryptocurrency keys in an attempt to be more secure than storing keys on Internet-connected devices.

Ledger has claimed that the targeted wallets appear to have been sold via CryptoBilis, a Southeast Asian reseller that operates in Indonesia, Malaysia, and the Philippines. Ledger said that at least one affected device "contained an unauthorized hardware implant". Several third party researchers disassembled affected hardware devices, finding that a chip and antenna had been added to capture crypto wallet seed phrases and transmit the data to the attacker using a cellular connection.

Pudgy Penguins company shuts down its Abstract blockchain after losing "8 figures" running it

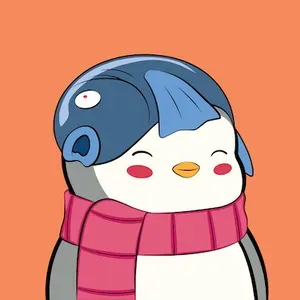
An illustration of a smiling penguin wearing a pink scarf with a blue dead fish on its head.Pudgy Penguin #6827 (attribution)
Igloo, the company behind the Pudgy Penguins NFTs, announced it will shut down Abstract, its Ethereum layer-2 blockchain, on December 15. CEO Luca Netz said the company had lost "8 figures" in the less than two years they were running the chain.

Users have until December 15 to move their assets, after which anything left on the chain will become inaccessible. DefiLllama estimates there were around $76 million in assets on the chain when the shutdown was announced, leading some users to complain that the wind-down period is too short.

The shutdown comes a few months after Igloo shut down its Pudgy Party mobile game, which had dropped to around 200–300 active users shortly after its launch, and also lost the company millions of dollars.

Blur shuts down its Blast blockchain

Blast, the Ethereum layer-2 created by the team behind the Blur NFT marketplace, is shutting down less than three years after launch. In the announcement, they disclosed that its costs now exceed its revenue and that it sees "no credible path" to fixing that. Despite once boasting of more than $2 billion in total value locked in June 2024, generating revenue from network usage of around $3.5 million, that revenue has collapsed to less than $2,000 last month.

Porsche shuts down its NFT project with the floor price down 96%

When Porsche announced its Porsche 911 NFT project at Art Basel Miami in 2022, it promised holders "he opportunity to co-create Porsche's future in the Web3 universe". Turns out there wasn't much to that future.

After bungling the mint, selling fewer than 2,000 of the planned 7,500 NFTs after buyers balked at the 0.911 ETH (then $1,490) pricetag, the price went nearly exclusively downhill. Now, with the NFTs floundering with floor prices down 96% from launch, Porsche has announced it is ending its "shared adventure".

Near Intents exploited for $3.8 million, recovers all assets

Near Intents, a cross-chain swap service, halted operations after an attacker drained around $3.8 million by exploiting a bug in its Omni layer.

The next day, Near Intents posted addresses for returning the funds and threatened the attacker: "We have identified you, sir." The attacker returned everything the next day, in a transaction that included an on-chain message saying "We've returned all the funds, we were in the wrong". Near Intents confirmed the funds were returned, and said they were stopping their investigation.

Abracadabra proposes winding down after string of hacks years ago left each $1 "stablecoin" token backed by $0.04 in reserves

Abracadabra, the defi project behind the Magic Internet Money (MIM) stablecoin, is shutting down. It blamed its string of hacks: $6.5 million theft in January 2024, $13 million in March 2025, and $1.8 million in October 2025, which altogether left about $21 million in bad debt. According to the shutdown proposal, 22 million MIM are in circulation, backed by just $900,000 in "actionable backing" which puts the supposedly dollar-pegged token at about $0.04. Two wallets voted on the proposal.

In June, a similarly low-participation vote handed "stewardship" of the project to a different group which promised to "revitalize" Abracadabra. Days later, treasury wallets sold around $500,000 worth of MIM. In July, the project tweeted that a roadmap to restore the peg was "coming this week," then never posted again. A week after that tweet, Abracadabra-controlled wallets moved about $8.3 million in treasury assets with no explanation, some of it to a Binance deposit address, in what one commentator called "treasury looting". The wind-down proposal doesn't mention the $8.3 million or count it toward what MIM holders could redeem.